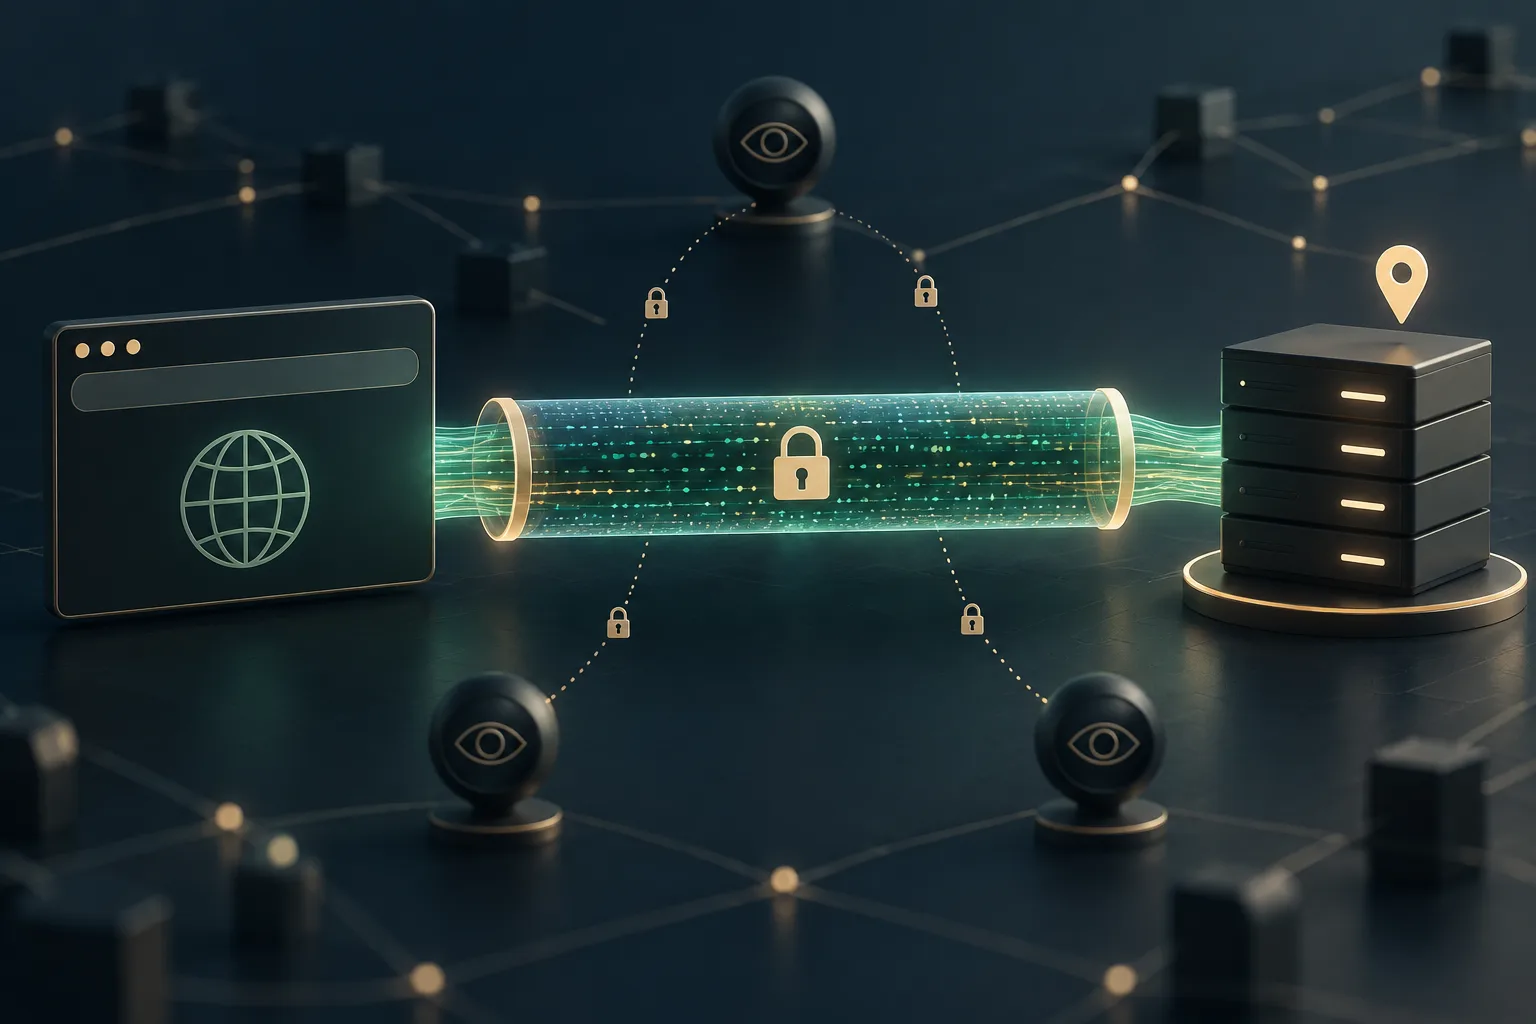
Before a browser opens a website, it usually needs to translate the domain name into a network address. That lookup is handled by the Domain Name System, or DNS. Traditional DNS often sends the question in plain text, giving nearby network operators a clear view of the names your device asks to reach.
DNS over HTTPS changes that path by placing DNS messages inside an encrypted HTTPS connection. It closes a meaningful privacy gap. It does not make the rest of your browsing invisible.
DNS over HTTPS privacy protects the lookup
DNS over HTTPS, commonly called DoH, encrypts queries between your browser or operating system and a compatible DNS resolver. The MDN definition of DNS over HTTPS explains that this prevents on-path parties from reading or modifying domain-name requests in transit.
Without encrypted DNS, someone controlling the local Wi-Fi, internet connection, or another point along the route may see that your device requested example.com. They may also tamper with the reply and redirect you. DoH makes the query and response look like protected HTTPS traffic between you and the chosen resolver.
The protection is specific. It covers the name-resolution exchange. The resulting website connection has its own encryption, routing, and metadata, which must be considered separately.
What DoH hides from the local network
A person observing ordinary DNS traffic can often assemble a useful list of requested domains. That list may reveal news sources, workplaces, health services, financial providers, or religious sites even if the pages themselves use HTTPS. DoH prevents that observer from simply reading the DNS question.
It also protects the resolver’s answer from casual manipulation along the path. The IETF standard RFC 8484 defines how DNS queries and responses are carried over HTTPS, inheriting the confidentiality and integrity properties of that channel.
This is valuable on hotel, airport, café, and shared-building networks. It also helps at home, where conventional DNS may otherwise be visible to the internet provider or whoever manages the router.
What DNS over HTTPS does not hide
DoH is sometimes described with language that makes it sound like a small VPN. It is not. It encrypts DNS traffic to one resolver; it does not reroute every web connection through a private tunnel.
The destination resolver sees the query
Encryption moves trust. Your local network can no longer read the DNS question, but the DoH resolver receives it in order to answer. The resolver may see your source network address, the requested domain, and timing information, subject to its technical setup and privacy policy.
Choosing a resolver is therefore part of the privacy decision. Look for clear statements about logging, retention, data sharing, filtering, and jurisdiction. A familiar brand is not a substitute for a readable policy.
Network metadata may still reveal destinations
After DNS resolution, the browser connects to a server address. Network observers can often see the destination IP address, traffic volume, and timing even when HTTPS protects page contents. Several websites may share one address, while some services use distinctive infrastructure, so the inference is imperfect but still useful.
Other connection details can also expose information depending on the protocol and deployment. Encrypted Client Hello is designed to protect more of the TLS handshake, but support and configuration are separate from DoH. Enabling one does not guarantee the other.
The website still knows you arrived
The destination site receives the request. It can associate activity with an account, cookies, browser characteristics, and its own logs. DoH does not block trackers embedded in the page. Our guide to how tracker blocking changes the web covers that different layer.
DoH, HTTPS, private browsing, and VPNs
These tools solve different problems, and their names are easy to collapse into a single idea of “private browsing.” A clearer model is to ask which part of the route each tool protects.
- DoH encrypts DNS questions between the client and resolver.
- HTTPS encrypts web traffic between the browser and website.
- Private browsing mainly limits what the browser keeps locally after the session.
- A VPN encrypts device traffic to a VPN endpoint and changes which network intermediary sees the onward connection.
None of these makes an account anonymous to the service you sign into. Our article on private browsing and retained data explains why a clean local history is not the same as invisibility to websites or providers.
Why networks sometimes interfere with encrypted DNS
Managed workplaces, schools, and family networks may depend on DNS for threat blocking, internal hostnames, or policy enforcement. A browser that silently bypasses the designated resolver can break those functions. Captive portals can also complicate encrypted DNS before a network login is complete.
Modern browsers often use fallback rules or managed policies in these environments. That means the setting may behave differently across networks. If internal services stop resolving, check whether the device is managed before forcing a resolver change.
A failure to use DoH should be visible rather than mysterious. Users deserve to know whether queries are encrypted, have fallen back to traditional DNS, or are governed by an organization’s policy.
How to choose a DoH resolver
- Read the logging policy. Check what is stored, how long it stays, and whether data is shared.
- Confirm security features. Some resolvers block known malicious domains; others provide unfiltered answers.
- Consider jurisdiction. The resolver operates under the laws where it is based and where infrastructure runs.
- Measure reliability. Privacy settings that frequently fail or add large delays may push users toward unsafe workarounds.
- Know the fallback. Determine whether the browser uses ordinary DNS when the encrypted resolver is unavailable.
Reviewing the resolver is similar to reviewing any browser grant: identify the exact data flow, choose deliberately, and revisit the decision when circumstances change. The same method appears in our guide to browser permissions.
A sharper expectation for encrypted DNS
DNS over HTTPS improves privacy because domain lookups should not travel as open postcards. It reduces local surveillance and makes simple DNS tampering harder. That is a worthwhile default when implemented transparently.
But the resolver still answers the question, the network still carries a connection, and the destination site still sees the visit. Treat DoH as one well-defined layer in a larger privacy system. Choose the resolver with care, combine it with HTTPS and tracker protection, and keep its limits in view.
Browse with more intention
Noorani brings prayer times, Qibla, tracker blocking, and privacy into one calm desktop browser built for how Muslims live online.